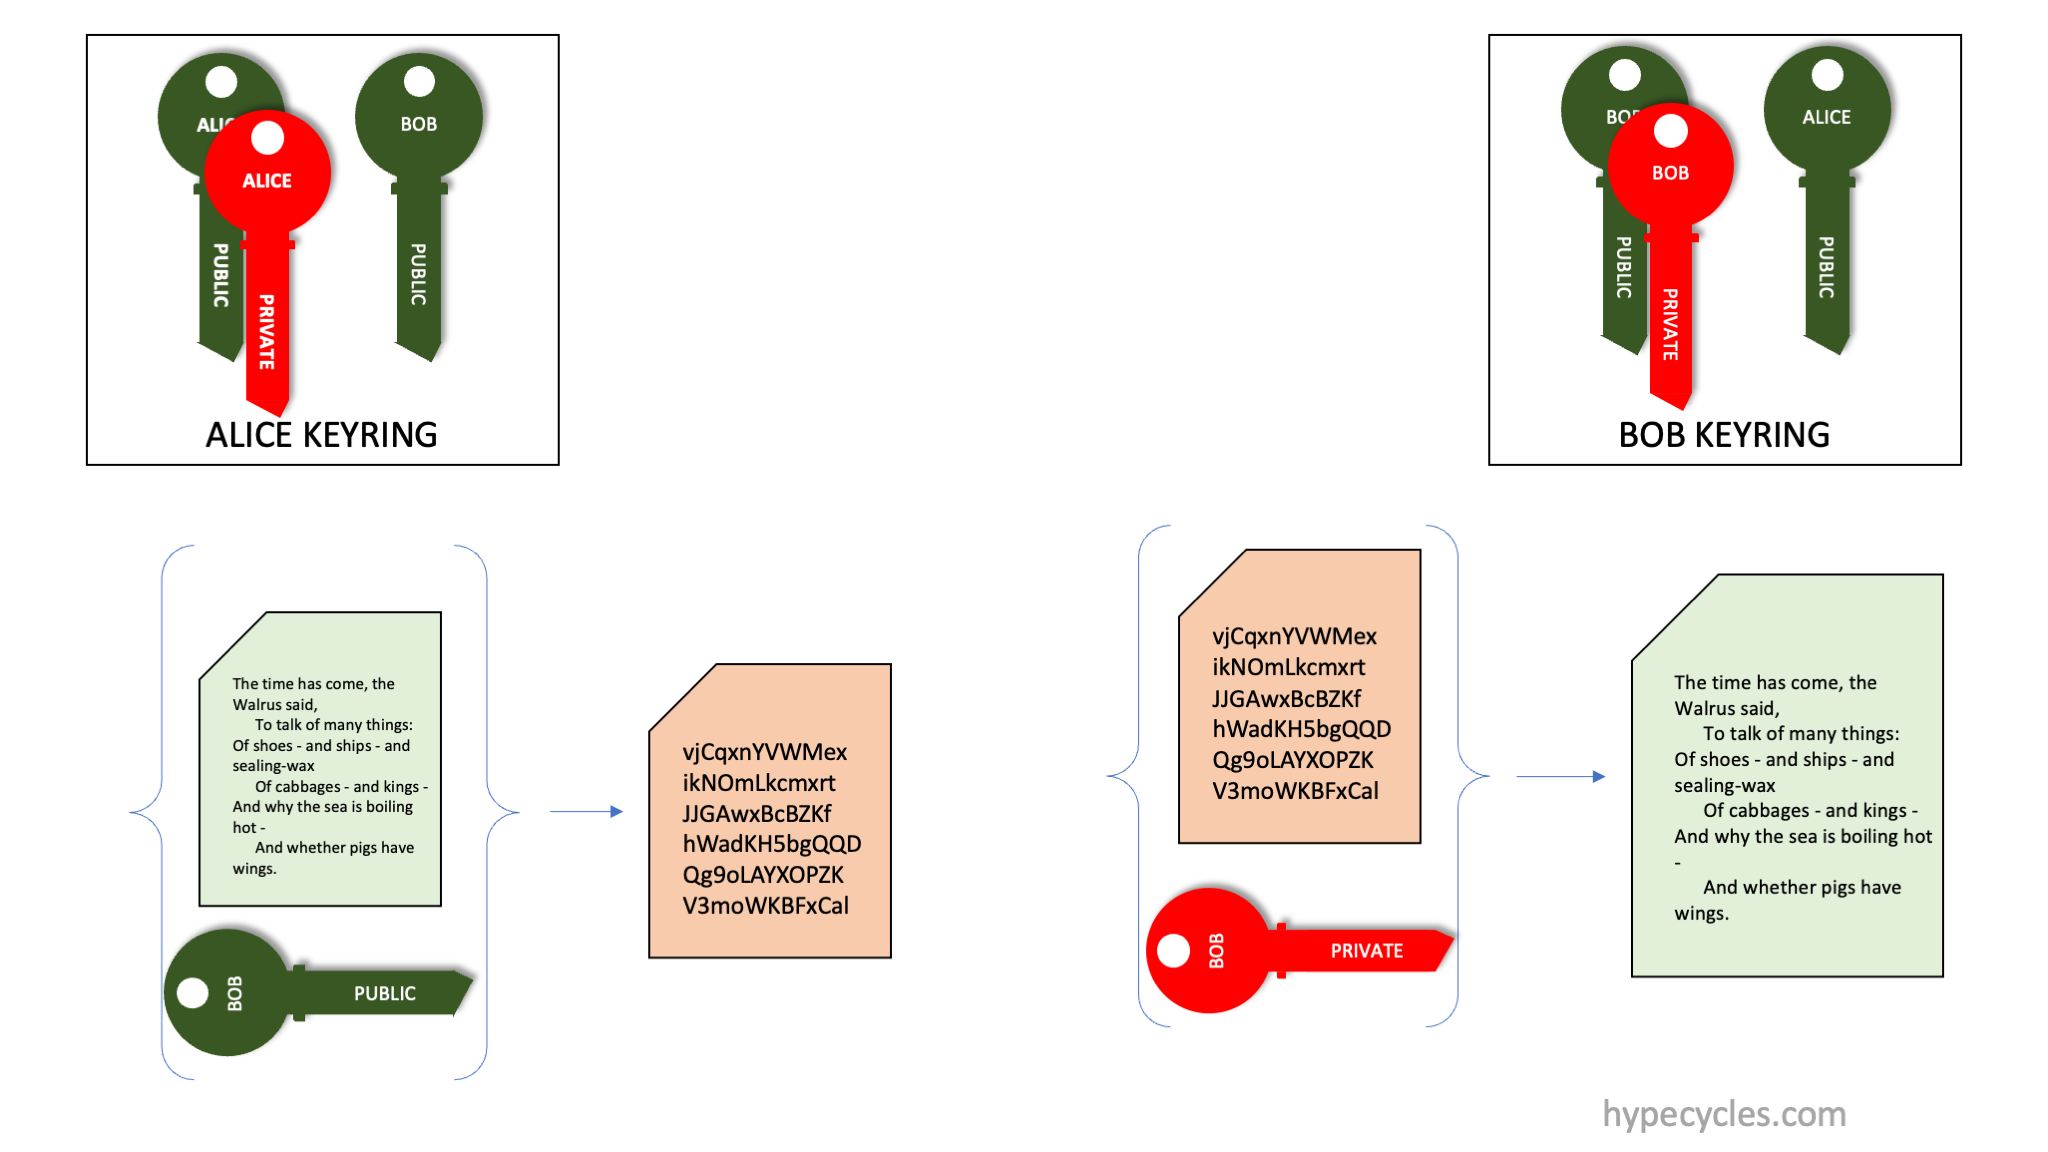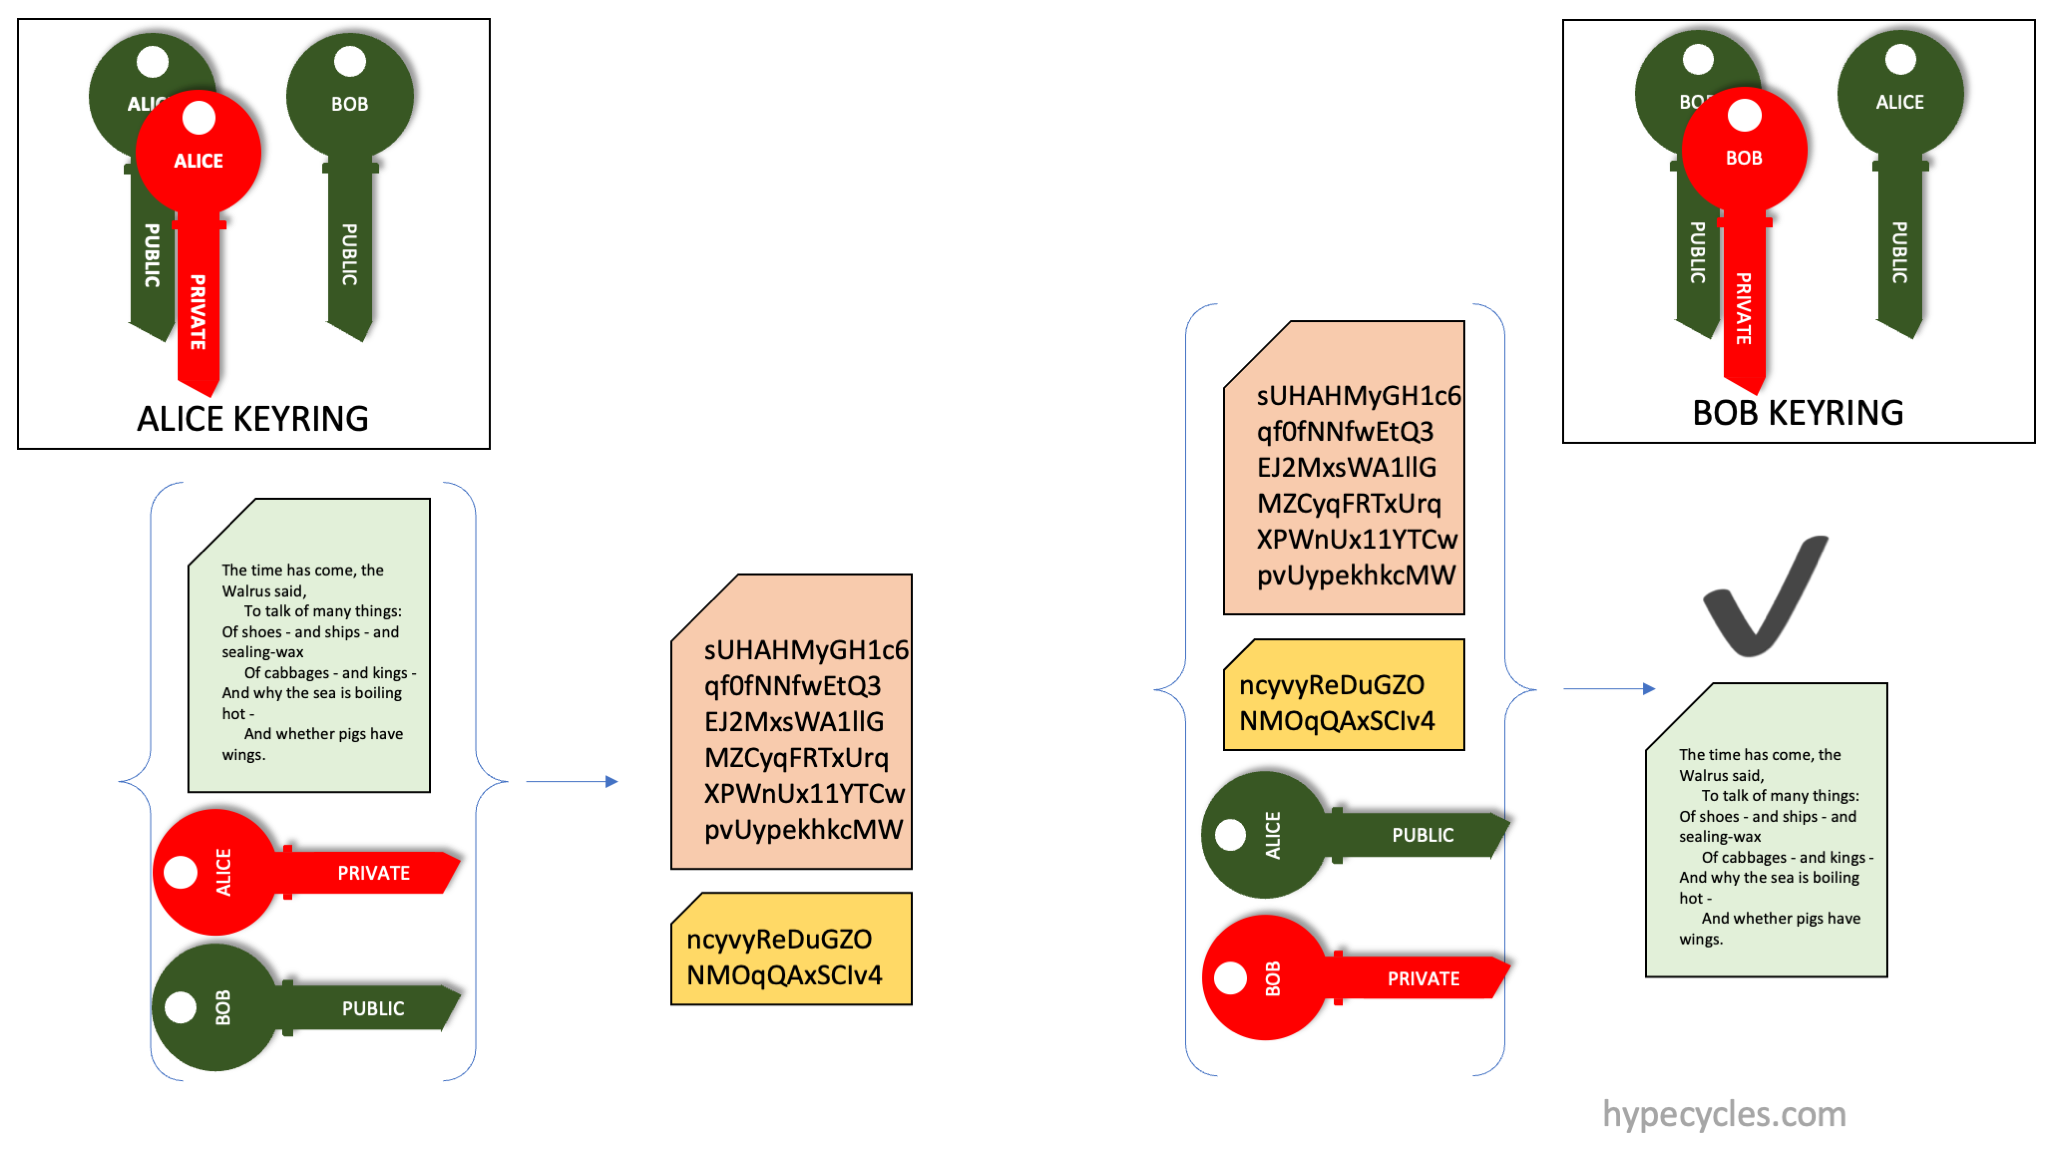
This fall, AI systems produced, or helped produce, claimed solutions to problems that had been open for decades. One, the Riemann Hypothesis, had stood for 167 years. Some are among the Clay Mathematics Institute’s Millennium Prize Problems, each worth $1 million. P vs NP is another problem on that list. OpenAI says it began running a model on all the open Millennium problems on September 1. That includes P vs NP, but OpenAI has published nothing specific about it. This post looks at what would follow from each possible answer.
The short version: as far as I can tell, nothing you rely on has broken. The one thing to act on is old 1,024-bit RSA keys, which have become cheaper to attack and should be replaced. In my opinion, a proof that P ≠ NP would change little in daily life. A proof that P = NP would matter a great deal in practice only if it came with an algorithm practical enough to use. I think that is the least likely outcome.
The question
Roughly, the question is whether every problem whose answers are easy to check is also easy to solve.
P and NP are sets of problems. Each set contains yes-or-no questions, such as “Is this list in order?” or “Can this puzzle be solved?”
P is the set of yes-or-no problems that a step-by-step algorithm making no random choices can solve in polynomial time. Polynomial time means the number of steps grows no faster than some fixed power of the input size n, such as n2 or n3, even on the worst inputs. “Is this list in order?” is in P, since one pass through the list answers it. So is “Is there a route between these two points on the map shorter than 10 miles?” because the shortest route can be found in polynomial time. Testing whether a number is prime is also in P, in time polynomial in its number of digits. Manindra Agrawal, Neeraj Kayal and Nitin Saxena proved this in 2002.
In this post, “fast” means polynomial time, and “practical” means quick enough to run on real inputs. A polynomial-time algorithm can still be far too slow to use.
NP is the set of yes-or-no problems where every “yes” answer comes with evidence that can be checked fast. No “no” answer has evidence that passes the check. Sudoku is the usual picture. Checking a filled-in grid is fast. Completing a large, partly filled grid, as far as anyone knows, is not.
Every problem in P is also in NP, because a checker can ignore the evidence and solve the problem itself in polynomial time. So P is a subset of NP. What nobody knows is whether the two sets are equal, or whether NP contains problems that are not in P.
The hardest problems in NP are called NP-complete. A polynomial-time algorithm for any one of them would give polynomial-time algorithms for all of NP.
Stephen Cook made the question precise in 1971. Leonid Levin, working independently, published the same ideas in 1973. The Clay Institute still lists it as unsolved.
Factoring and today’s public-key cryptography
Factoring means taking a whole number larger than 1 and finding the primes that multiply to give it. The question “Does this number have a factor larger than 1 and smaller than k?” is in NP. If someone hands you such a factor, you can check it with one division.
Factoring matters because RSA, one of the most widely used public-key systems, depends on it being hard. The other widely used family, elliptic-curve cryptography, depends on a related hard problem. Together they secure most web connections and the signatures on most software updates today. Many browser connections now also add a post-quantum key exchange, but certificates still rely on RSA or elliptic curves.
Nobody knows whether factoring is in P. The best known method for ordinary computers is the general number field sieve. Its running time is believed to grow faster than any polynomial in the number of digits, but slower than exponentially. With it, researchers factored a 250-digit RSA challenge number in 2020, using about 2,700 years of single-core computer time.
This fall, the record moved, with AI help. On September 3, Eric Lu of the AI company Cognition factored a 260-digit challenge number. He used sieve software rebuilt for graphics processors with help from Cognition’s AI agent, Devin. Sixteen days later, Stephen Weis of Anthropic factored RSA-896, a 270-digit number and the largest RSA challenge number factored so far. He had used Claude to port the open-source sieve program CADO-NFS to graphics processors. Lu factored a slightly smaller 270-digit number in November. Weis says the work did not make the method itself meaningfully faster. Real RSA keys are usually 2,048 bits, about 617 digits.
Researchers doubt that factoring is NP-complete. Factoring is also in coNP, the set of problems whose “no” answers come with evidence that can be checked fast. The full list of prime factors is that evidence. If factoring were NP-complete, NP would equal coNP, and most researchers think the two are different. So factoring probably sits between P and the NP-complete problems. A proof that P = NP would put factoring in P, because factoring is in NP. A proof that P ≠ NP would not tell us that factoring is hard.
Quantum computers are a separate threat. In 1994, Peter Shor found an algorithm that factors numbers, and solves the problem behind elliptic-curve cryptography, in polynomial time on a large enough quantum computer. No quantum computer today is close to large enough. That threat is why governments and companies are moving to post-quantum cryptography, which I come back to below.
Symmetric (shared-key) ciphers such as AES encrypt data once two parties share a key. They don’t rely on factoring or the elliptic-curve problem. They still rely on something being hard to compute, which matters in the P = NP section below. The best known quantum attack on AES, Grover’s algorithm, gives only a quadratic speedup, which doubling the key length offsets.
What happened this fall
September 1: OpenAI’s run on the open Millennium problems began, according to OpenAI.
September 3 and 19: AI-assisted efforts set new records for factoring RSA challenge numbers (details above).
September 8: OpenAI claimed a solution to the Navier–Stokes Millennium problem, in the two versions that allow an external force.
October 5 and 6: AI-found algorithms were claimed to beat several long-standing guesses about the best possible running times for certain problems (details below).
October 6: OpenAI released 722 manuscripts on open problems. They include partial results on the Riemann, Birch–Swinnerton-Dyer and Hodge problems, and a proposed proof of the Unique Games Conjecture. OpenAI withdrew three of the manuscripts within a day.
October 26 and 27: OpenAI and Anthropic separately claimed to have refuted the Exponential Time Hypothesis, a widely used assumption in computer science. OpenAI also claimed a proof of the existence part of the Yang–Mills Millennium problem, but not its “mass gap” part.
November 6: Google DeepMind reported AI-found methods that make old 1,024-bit RSA keys cheaper to attack.
November 20: Levent Alpöge, a mathematician at Anthropic, released a proof of the Riemann Hypothesis that he says he found working with Claude.
November 21: The Lean and Mathlib proof-checking communities certified Alpöge’s proof.
The Exponential Time Hypothesis. 3-SAT is a standard NP-complete problem. You get a list of true/false variables and many small rules, each involving three of them. You have to decide whether some setting of the variables satisfies every rule.
The hypothesis was proposed in the late 1990s by Russell Impagliazzo and Ramamohan Paturi, partly in work with Francis Zane. It says there is a fixed number k such that every algorithm’s worst-case time for 3-SAT at least doubles with every k added variables. Before this fall, the best algorithms that make random choices took about 1.31n steps for n variables, which doubles roughly every 2.6 variables. Hundreds of papers used the hypothesis to argue that some problem has no algorithm much faster than the best known one. Impagliazzo himself said in 2012 that he and Paturi thought it was “about a fair coin flip” whether this hypothesis and a stronger version of it were true.
Both labs claim algorithms whose time bound grows more slowly than any fixed doubling rate, though it still grows faster than any polynomial. The hypothesis says no such algorithm exists. Even if the claims hold, they don’t show that P = NP. Anthropic says its result tells us nothing about solving formulas in practice.
Both claims come with proofs in Lean, a language in which a computer program checks every step of a proof. Outside researchers have rerun both through Lean’s checker. The Anthropic proof also passed a second, independently written checker, and a port of the OpenAI proof later passed several. One researcher reported that, according to Lean, each lab’s theorem refutes the hypothesis as defined in ComplexityLib, a shared Lean library. Whether that definition matches the original hypothesis still needs expert reading. OpenAI’s Lean theorem proves a weaker bound than its paper claims, though still enough to refute the hypothesis as that library defines it.
OpenAI asked Impagliazzo, Paturi and MIT’s Ryan Williams to lead a review, which now covers both labs’ claims. As of November 19, it was still under way.
Other speed limits. A “speed limit” here means a guess that no algorithm can beat a certain running time. In early October, AI-found algorithms were claimed to break several:
3SUM asks whether any three numbers in a list of n numbers add up to zero. A textbook method takes about n2 steps, and researchers had assumed the exponent 2 could not be lowered at all. A paper by Josh Alman and Virginia Vassilevska Williams, posted October 5, explains an algorithm found by an Anthropic model. The algorithm takes about n1.9992 steps. The gain is tiny in practice: for a trillion numbers, that is only about 2% fewer steps than n2, before overheads.
All-pairs shortest paths means finding the shortest route between every pair of points in a network. The same algorithm also solves it in about n2.9995 steps instead of about n3, for networks whose distances are integers that aren’t astronomically large.
Multiplying two n-digit numbers was conjectured in 1971 to need about n log n steps. (The base-2 logarithm grows very slowly: for a million-digit number it is about 20.) A method reaching that bound was found in 2019. OpenAI’s October 6 release claims to beat it.
The Riemann Hypothesis. Bernhard Riemann stated it in 1859. It predicts where certain zeros of a function lie, which governs how evenly the prime numbers are spread out. The way Alpöge’s proof was checked shows how AI-assisted proofs of famous problems get vetted. The proof is about 17 million lines of Lean. Mathlib is Lean’s shared math library. On November 21, the Lean and Mathlib communities said in a joint statement that they “certify that both the statement and the proof of the Riemann Hypothesis are correct.” Two separate tools confirmed that the theorem proved is exactly Mathlib’s vetted statement of the hypothesis, and several independently written checkers accepted the proof.
Apart from a short note, Alpöge has released only the Lean code, and no traditional journal paper has been published. The Clay Institute’s rules require publication in a qualifying outlet, a two-year wait and general acceptance. The Institute still lists the problem as open.
On November 20, the day Alpöge released his proof, AI helped find problems in a human-written proof of a related conjecture. Ravi Vakil, president of the American Mathematical Society, posted Alessandro Masullo’s proposed proof of the Generalized Riemann Hypothesis, a broader form of the Riemann Hypothesis. About eight hours later, Vakil reported that several people, helped by AI models, had found problems in it.
If P equals NP
How much a proof of P = NP would matter depends on what the proof provides.
If it comes with a practical algorithm, the effects would be enormous. Picture an algorithm that solves 3-SAT in something like n3 steps, with modest constants (the fixed multipliers and overheads in the step count).
Almost all cryptography in use today needs a one-way function: something easy to compute and hard to reverse, like scrambling a password into a hash. It is a theorem that one-way functions can exist only if P ≠ NP. With a practical algorithm for NP problems, an attacker could in principle factor the numbers in RSA public keys and recover elliptic-curve keys. The same holds for symmetric ciphers such as AES. Given a short piece of known plaintext, a guessed key can be checked fast, so finding the key is an NP problem. How practical is practical enough would depend on the details, since a key-recovery problem rewritten in 3-SAT form can have millions of variables.
If the algorithm were practical enough to recover real keys, the only encryption sure to survive would be the kind that doesn’t depend on anything being hard to compute. The one-time pad is an example. It needs a shared secret key as long as the message. Traffic recorded today would be exposed too, including traffic protected by AES or post-quantum schemes.
Post-quantum cryptography would not help. Post-quantum schemes, such as ML-KEM and ML-DSA, the lattice-based standards NIST published in 2024, rest on problems believed to be hard even for quantum computers. That protects them against Shor’s algorithm. It does not protect them against a practical algorithm for NP. A guessed key can still be checked fast against the public key, so recovering a key is still an NP problem. A practical algorithm for NP would recover it. Quantum computers are not believed to solve NP-complete problems fast, so a problem can be hard for them and still be in NP. “Hard for quantum computers” and “hard even if P = NP” are different promises. Post-quantum cryptography makes only the first.
The benefits would be large too. Many scheduling, routing and chip-design problems are NP-complete. These problems, and versions of them that ask for the best answer, would become practical to solve exactly.
Mathematics would change as well. Checking a formal proof is fast. So the question “Is there a proof of this statement at most n symbols long?” is an NP problem, if n counts as part of the input’s size. Kurt Gödel raised essentially this question in a 1956 letter to John von Neumann. He wrote that if a machine could answer it in roughly n or n2 steps, a mathematician’s work on yes-or-no questions “could be completely replaced by a machine.” With a practical algorithm, finding proofs of modest length would become routine.
If the algorithm is impractical, little would change right away. Computer science already has “galactic” algorithms that beat everything else only on inputs too large to ever occur. A proof of P = NP could give an algorithm that takes n1000 steps.
Donald Knuth said in a 2014 interview that he believed P = NP, but that a proof “will almost surely be nonconstructive.” Such a proof would show that some algorithm runs in nM steps for a huge, unknown M, without saying what the algorithm is. Even then, we would have one explicit, if useless, method. Levin’s “universal search” (1973) runs every possible program side by side. If P = NP, it would find solutions to NP problems that have them, keys included, in polynomial time. Its overheads, though, are far too large for it ever to finish on real inputs. Existing encryption would keep working, but its safety would rest on nobody finding a practical algorithm.
If P does not equal NP
P ≠ NP is the outcome most researchers expected before this fall. In William Gasarch’s poll of 124 respondents, taken in 2018 and published in 2019, 88% said P ≠ NP. Among those he judged to be experts, 99% did. I know of no poll taken since these results appeared.
It would not, by itself, make cryptography safe. P ≠ NP says that for some problems in NP, every fast algorithm fails on some inputs. Cryptography needs more. It needs a way to generate puzzles that are hard to solve in typical cases while the person who made them knows the answer.
Impagliazzo laid out the possibilities in a 1995 paper as five “worlds.” A proof of P ≠ NP would rule out the world where every NP problem has a fast algorithm, at least for algorithms that make no random choices. The other four remain. Three of them would be bad news for cryptography:
- a world where hard cases exist but are rarely met;
- a world where nobody can generate hard puzzles with known answers;
- a world where shared-key encryption works but public-key systems, which let strangers communicate securely over the web, don’t.
- The fourth is the world today’s cryptography assumes, where public-key encryption works.
Factoring shows in a concrete case how far P ≠ NP falls short: as described above, P ≠ NP would not show that factoring is hard. The lattice problems behind most post-quantum schemes are in a similar position. Proofs link these schemes’ security to finding a lattice vector that is only roughly the shortest, within a factor that grows with the lattice’s dimension. At those factors, the yes-or-no version of that problem is known to be in coNP as well as NP. So, like factoring, it is not believed to be NP-complete. A proof of P ≠ NP would not show it is hard even in the worst case, let alone in typical ones.
It also would not mean computers can’t handle NP-complete problems in practice. SAT solvers are programs that solve logic puzzles like 3-SAT, and they are used to check chip designs and software. They often handle industrial problems with millions of variables. P ≠ NP would say that no fast algorithm works on every input. It would say nothing directly about the inputs people actually give these solvers.
The proof would have to contain new ideas. Researchers have shown that three broad families of proof techniques can’t prove P ≠ NP. For one family, the barrier holds only if a standard cryptographic assumption is true. In 2011, Ryan Williams got around at least two of these barriers on a weaker question, which shows they can be avoided in some settings.
What this means for you today
For encryption at today’s recommended key sizes, I have found no sign of weakening from this fall’s results. You don’t need to rotate keys, reissue certificates or change TLS settings because of them.
The exception is old 1,024-bit RSA keys. Standards bodies retired them years ago, but they still turn up in legacy systems. No properly generated 1,024-bit RSA key is known to have been factored. After factoring RSA-896, though, Weis wrote that such keys are vulnerable to many actors with data-center-scale fleets of graphics processors. On November 6, Google DeepMind reported that AI agents had cut the cost of forging 1,024-bit RSA signatures in some settings and of factoring many such keys at once. If you still have 1,024-bit RSA keys, replace them.
The new 3-SAT algorithms are far too slow to threaten real systems. SAT solvers and optimization tools work the same as before.
If your company is moving to post-quantum cryptography, keep going. That work protects against future quantum computers, which would threaten RSA and elliptic-curve systems however P vs NP turns out. It does nothing against a practical P = NP algorithm.
In my view, a more likely risk than a P = NP proof is an AI-found attack on one specific scheme. The DeepMind results on 1,024-bit RSA are one example. Earlier this year, Anthropic reported that one of its Claude models had found an improved attack on HAWK, a candidate post-quantum signature scheme that is not deployed. For the smallest version of HAWK, the attack lowers the estimated work to recover a key from about 264 to about 238 operations. Anthropic says the attack “does not impact other NIST post-quantum signature candidates or lattice-based cryptography in general.” In a footnote, Anthropic adds that it believes the attack does not affect the other NIST post-quantum schemes, which include ML-KEM and ML-DSA. Individual schemes have fallen suddenly before, without AI. In 2022, researchers broke SIKE, another post-quantum candidate, with an attack that recovered keys for its smallest version in under an hour on a single computer core. This is one reason browsers pair a post-quantum key exchange with a classical one, so an attacker would have to break both.
What I think
What follows is my opinion. The main sources for its facts are listed at the end.
Why I still think P ≠ NP
People have spent more than 50 years looking for a fast algorithm for any of thousands of NP-complete problems. None has turned up.
I am less sure than I was in September, though. The claimed refutation of the Exponential Time Hypothesis moves me little by itself. Two of the hypothesis’s authors had called it about a coin flip whether it and a stronger version were true. Several such results arriving together move me more. Within a few weeks, AI systems produced claimed algorithms for 3SUM, all-pairs shortest paths, integer multiplication and 3-SAT. (The first two came from a single algorithm.) Each beat a limit that experts had guessed was real.
The case for P = NP
That run of results is the core of the strongest case against my view. Emanuele Viola has argued for P = NP since 2018. He made the case again in an essay for BLOG@CACM, the blog of the magazine Communications of the ACM, and reposted it on his own blog on November 17. He writes that this fall’s results support his belief and cites three: the 3SUM algorithm, the faster multiplication method and the claimed refutation of the Exponential Time Hypothesis. In his words, researchers have “consistently underestimated the power of efficient computation.”
I agree with that part. But 3SUM and multiplication already had polynomial-time algorithms, and the new results only make them faster. The two 3-SAT algorithms still take more than polynomial time. I read these results as good evidence that experts underestimate what algorithms can do. I read them as weak evidence about whether NP-complete problems have polynomial-time algorithms.
Will AI settle it?
My guess is that AI will break more speed-limit conjectures before anyone settles P vs NP. This fall’s speed-limit results were all new algorithms, and AI systems have been good at finding algorithms. Proving P ≠ NP means ruling out every fast algorithm for an NP-complete problem, and that is where the known barriers apply.
AI has also produced claimed hardness results. One example is OpenAI’s proposed proof of the Unique Games Conjecture, released October 6. It would show that approximating certain problems beyond a set accuracy is at least as hard as every problem in NP. So it can’t be done fast unless P = NP. That kind of result is conditional and doesn’t face the barriers above. So it doesn’t directly test my distinction between finding algorithms and ruling them out. It does show that AI systems aren’t limited to finding new algorithms, which is one reason that distinction is only a hunch.
If a practical algorithm for NP-complete problems exists, I would expect AI systems to have the best chance of finding it. So years of searching without one would count, to me, as mild evidence that no practical algorithm exists.
My ranking
This is a guess. P ≠ NP is most likely, and P = NP with an impractical algorithm is second. P = NP with a practical algorithm is a distant third, and only the third would change daily life soon. If P ≠ NP is proved, I expect the new proof methods to matter more than the verdict, which most researchers already believe.
Checking and understanding
I think a machine-checked proof of a carefully vetted statement should count as a theorem. I don’t think it should count as understanding. Many mathematicians put understanding first. They include 28 winners of the Fields Medal, often called mathematics’ top prize, who have signed a declaration posted on September 11. The declaration warns that AI companies’ push to solve famous problems could undermine the goal of understanding. I take their view seriously. I expect it will be years before anyone can explain why the Riemann Hypothesis is true.
I also can’t say what a machine that finds proofs is doing. The split between finding and checking is old. Thomas Aquinas wrote that human reasoning advances “by way of inquiry and discovery” from first principles. Then, “by way of judgment,” it returns to them, “in the light of which it examines what it has found” (Summa Theologiae I, q.79, a.8). In that article, he does not say which of the two is harder. For him, discovery is reasoning in steps, but each step moves from one thing understood to the next. On that view, just carrying out steps is not enough for discovery.
Pope Leo XIV’s 2026 encyclical Magnifica Humanitas, a formal papal letter, says AI systems “do not understand what they produce.” The reason it gives is that they lack “the affective, relational and spiritual perspective through which human beings grow in wisdom” (§99). The encyclical treats this as settled, on the basis of its account of the human person. It also says that the internal workings of these systems “remain, at present, unknown” (§98). Among AI researchers and philosophers, I don’t think the question is settled.
I expect a P vs NP proof would be harder to vet than the Riemann proof was. Public formal statements of P vs NP exist, but none that I know of has been vetted the way Mathlib’s Riemann statement was. It is easy to write a Lean statement that looks like P vs NP but isn’t.
What I’ve said about this fall’s results assumes that Lean and the independent checkers are trustworthy. For the Riemann proof, I think that trust is justified, because several independently written checkers accepted it, and a bug shared by all of them is unlikely. Two of them also come with formal proofs, relative to set theory, that they cannot accept a false proof. For most of us, accepting a 17-million-line proof that no one has read in full is belief on testimony: we trust the people who report that the checkers accepted it. Augustine pointed out that we believe countless things on other people’s word, including who our parents are (Confessions VI.5). Checkers can’t tell us whether a formal statement means what we intend, though, which is why the human vetting step matters. If a checker were ever shown to have accepted a false proof in a high-profile case, I would have to give up that assumption.
A closing note
Whatever happens with P vs NP, AI has already changed how I work. I used to google to find things, and now I use AI to research things. That includes this blog post: I used an AI assistant, to help research, draft and check it.
The topics discussed above are of interest to me for two reasons. First, they are closely related to my “work life”. Second, I have long had a fascination for mathematics, which is also my educational background. Most of the “sources” listed below were in my RSS feed, or bookmark list, and my AI assistant already had them handy. But, I would not have been able to write this blog post without the assistance of my AI assistant.
I think AI will keep changing the world. It has changed the way in which we do software development. It is changing the way in which we do most other things these days. This fall showed that it has also changed how mathematics gets done.
Why should one believe that it won’t change our understanding of P = NP?
I wouldn’t normally read things published by religious organizations, but I heard about Magnifica Humanitas: Vatican on a podcast (from Robert Ballecer, the “Digital Jesuit”). I am fascinated by it, and think anyone deeply interested in Artificial Intelligence should read it.
Sources
- P vs NP and the prize: Clay Mathematics Institute, Millennium Problems; Clay, P vs NP; Clay rules
- P vs NP background, proof barriers and Levin’s universal search: Wikipedia, P versus NP problem
- Primality testing in P: Agrawal, Kayal and Saxena, “PRIMES is in P”
- Factoring, its complexity and the number field sieve: Wikipedia, Integer factorization
- Factoring records, RSA-250 through RSA-896: Wikipedia, RSA numbers; Stephen Weis, RSA-896
- Shor’s algorithm: Shor, FOCS 1994; expanded version arXiv:quant-ph/9508027. Grover’s algorithm, and why quantum computers are not expected to solve NP-complete problems fast: Wikipedia, Grover’s algorithm; Wikipedia, BQP
- Post-quantum standards: NIST, first post-quantum FIPS approved (2024)
- Lattice problems in NP and coNP: Aharonov and Regev, “Lattice problems in NP ∩ coNP” (PDF)
- Retirement of 1,024-bit RSA: NIST SP 800-131A Rev. 2 (PDF)
- Hybrid post-quantum and classical key exchange in browsers: Google Security Blog, A new path for Kyber on the web; Chromium Blog, Protecting Chrome traffic with hybrid Kyber KEM
- Badly generated 1,024-bit keys that were factored: Bernstein et al., ePrint 2013/599
- Lattice schemes’ security reductions: Regev, arXiv:2401.03703; Langlois and Stehlé, ePrint 2012/090
- DeepMind’s attacks on 1,024-bit RSA: SecurityWeek
- OpenAI’s Millennium work and Navier–Stokes claim: OpenAI, Navier–Stokes
- OpenAI’s October 6 release: Wikipedia, OpenAI bulk release of mathematical papers; Scientific American, on the release and cryptography
- Exponential Time Hypothesis and Yang–Mills claims, and the review: OpenAI, October 26 announcement; Anthropic, ETH paper and Lean proof; Wikipedia, Exponential time hypothesis; UC San Diego, independent review; ETH discussion blog, Lean replications thread; Emergent Mind, ETH explainer
- 3SUM and all-pairs shortest paths: Alman and Vassilevska Williams, arXiv:2610.06783
- Riemann Hypothesis proof: Lean and Mathlib joint statement; Scientific American
- Masullo’s proposed proof: Ravi Vakil’s announcement and update
- Gödel’s 1956 letter: English translation (PDF)
- Knuth: Twenty Questions for Donald Knuth, InformIT, 2014
- Expert opinion poll: Gasarch, SIGACT News, 2019 (PDF)
- Five worlds: Russell Impagliazzo, “A Personal View of Average-Case Complexity,” Proc. 10th Annual IEEE Structure in Complexity Theory Conference, 1995, pp. 134–147 (doi:10.1109/SCT.1995.514853)
- Williams’s 2011 result: Williams, “Nonuniform ACC circuit lower bounds” (PDF)
- HAWK attack: Anthropic, Discovering cryptographic weaknesses with Claude
- SIKE break (an attack on SIDH, the basis of SIKE): Castryck and Decru, IACR ePrint 2022/975
- Viola’s case for P = NP: What happened in fall 2026: AI and P vs NP
- Fields Medalists’ declaration: mathandai.org
- Aquinas: Summa Theologiae I, q.79 (New Advent)
- Magnifica Humanitas: Vatican
- Augustine: Confessions, Book VI (New Advent)